A privacy investigation into smart television tracking uncovered more than 57 million publicly accessible viewing detection records and found that several platforms continued transmitting traffic consistent with automatic content recognition after users disabled the feature.
The “Watching the Watchers” study examined 12 televisions from ten manufacturers across eight operating systems representing approximately 95% of the U.S. smart TV market.
Researchers ran 5,943 automated experiments to assess tracking behavior, opt-out effectiveness, and exposure of viewing data. The most significant exposure involved VIDAA, whose automatic content recognition system transmitted data to Unruly servers using unencrypted MQTT.
Smart TVs Expose 57 Million Viewing Records
Messages included a permanent, non-resettable device identifier, time zone, application name, input source, antenna channel, and audio fingerprints.
testbed (Source: watchingthewatchers)
watchingthewatchers found that the associated server required no authentication, allowing outsiders to access detection results from other televisions.
An ethically limited collection lasting about three hours yielded over 57 million records linked to more than 1 million unique televisions.
The results included 82 content categories, including politics, religion, and health and medicine. During controlled testing, playing “The Story of Moses” through HDMI produced a “Religious” classification.
Application metadata also exposed potentially sensitive interests. Researchers observed tracking involving VIDAA Kids, raising children’s privacy concerns, while another application transmitted television and film titles directly.
VIDAA confirmed the issue following disclosure. Authentication was subsequently introduced, but the researchers reported that messages remained unencrypted.
Upload traffic to the ACR endpoint (Source: watchingthewatchers)
The team also replayed a previously observed message, which reached its own test television. Researchers did not attempt to deliver a malicious payload, leaving the potential impact unverified.
Automatic content recognition identifies programming by matching audio or video fingerprints against reference libraries. Testing covered antenna broadcasts, streaming applications, HDMI connections, screen mirroring, and idle operation.
Opt-outs worked fully on tested implementations of LG webOS, Sony Google TV, Amazon Fire TV, and VIDAA.
Samsung’s Tizen continued producing traffic consistent with recognition in all 30 opted-out tests of its built-in streaming service. Residual traffic also appeared during antenna, HDMI, and Tubi viewing.
Vizio’s SmartCast showed no observable reduction in traffic to its identified Amazon Kinesis recognition endpoint after opting out. Roku’s controls did not cover its own streaming service.
Most recognition traffic was encrypted. Consequently, continued transmissions indicate behavior consistent with tracking, but do not confirm payload contents, server-side processing, or retention.
Vizio’s WatchFree+ exposed program or channel names through unencrypted DNS queries and TLS Server Name Indication associated with streaming provider Amagi. Network observers could reconstruct viewing sequences independently of recognition settings.
The findings apply to the tested devices and firmware, not all televisions. Researchers recommend authenticating and encrypting recognition traffic, independently auditing opt-outs, and removing viewing information from streaming hostnames. They also call for clearer disclosures identifying monitored inputs and applications.
Join 16,000+ SOC teams using ANY.RUN to streamline threat investigations and reduce manual effort. Explore for your team
A flaw in Signal’s calling library could let the other person on a call keep receiving a user’s audio, and possibly video, after that user hangs up. Tracked as CVE-2026-113380, the vulnerability affects RingRTC versions before 2.72.0. RingRTC is the open source library that powers voice and video calls in Signal’s apps, built on WebRTC, the technology browsers use for live audio and video. The CVE record states that “a peer that saturates a call’s … More →
GoDaddy has revoked 404,607 SSL/TLS certificates after discovering that certain subscriber certificates were issued outside the defined profiles in its Certification Practice Statement (CPS) and Certificate Policy (CP). The revocation took effect on October 21, 2026, requiring affected customers to obtain and install replacement certificates to avoid browser security warnings and potential website outages. This […]
The PHP security team released emergency security patches for two critical remote code execution (RCE) vulnerabilities (CVE-2026-109618 and CVE-2026-109619) tracked collectively as PHP2Shell. [...]
Amanda Smith answered the door one afternoon in April and came face to face with the local Sheriff’s department in upstate Pennsylvania. The officers said they had a warrant for her arrest for a crime she had allegedly committed more than a thousand miles away in Arkansas.
“I was completely confused,” Smith recalled. For one, she had never been to Arkansas. Second, the warrant was for computer fraud. By her own admission, Smith was not a very tech savvy person.
She had a feeling she was being set up. After discussing with the officers the practicalities of what was about to happen — she was allowed to get her contact lenses — they took her away in handcuffs to the local jail where she spent three nights.
The reason for Smith’s arrest, she learned later, was that a scammer had tricked someone on Facebook Marketplace into sending $1,000 to a CashApp account in her name that the scammer controlled. The scammer created the account using her Social Security number and date of birth. Smith said she has never used CashApp.
What developed over the next few days, and has now stretched across six months, is a Kafkaesque situation in which Smith, in her telling, is being asked to prove her innocence in an ongoing criminal case, while CashApp refuses to provide her any information about the account because she couldn’t prove that she was the owner.
The case shows the very real danger of identity theft, how the data and tools offered to police can lead them to the wrong person, and the sprawling world of CashApp fraud, where scammers and money launderers create or compromise accounts to make and move money quickly. Along the way, ordinary people may not just lose money, but their freedom too. Smith faces up to six years in prison for the charges.
“They're trying to turn it into my problem [...] that I need to prove that I'm innocent,” Smith told 404 Media. “That's not what I grew up believing was the way it worked.”
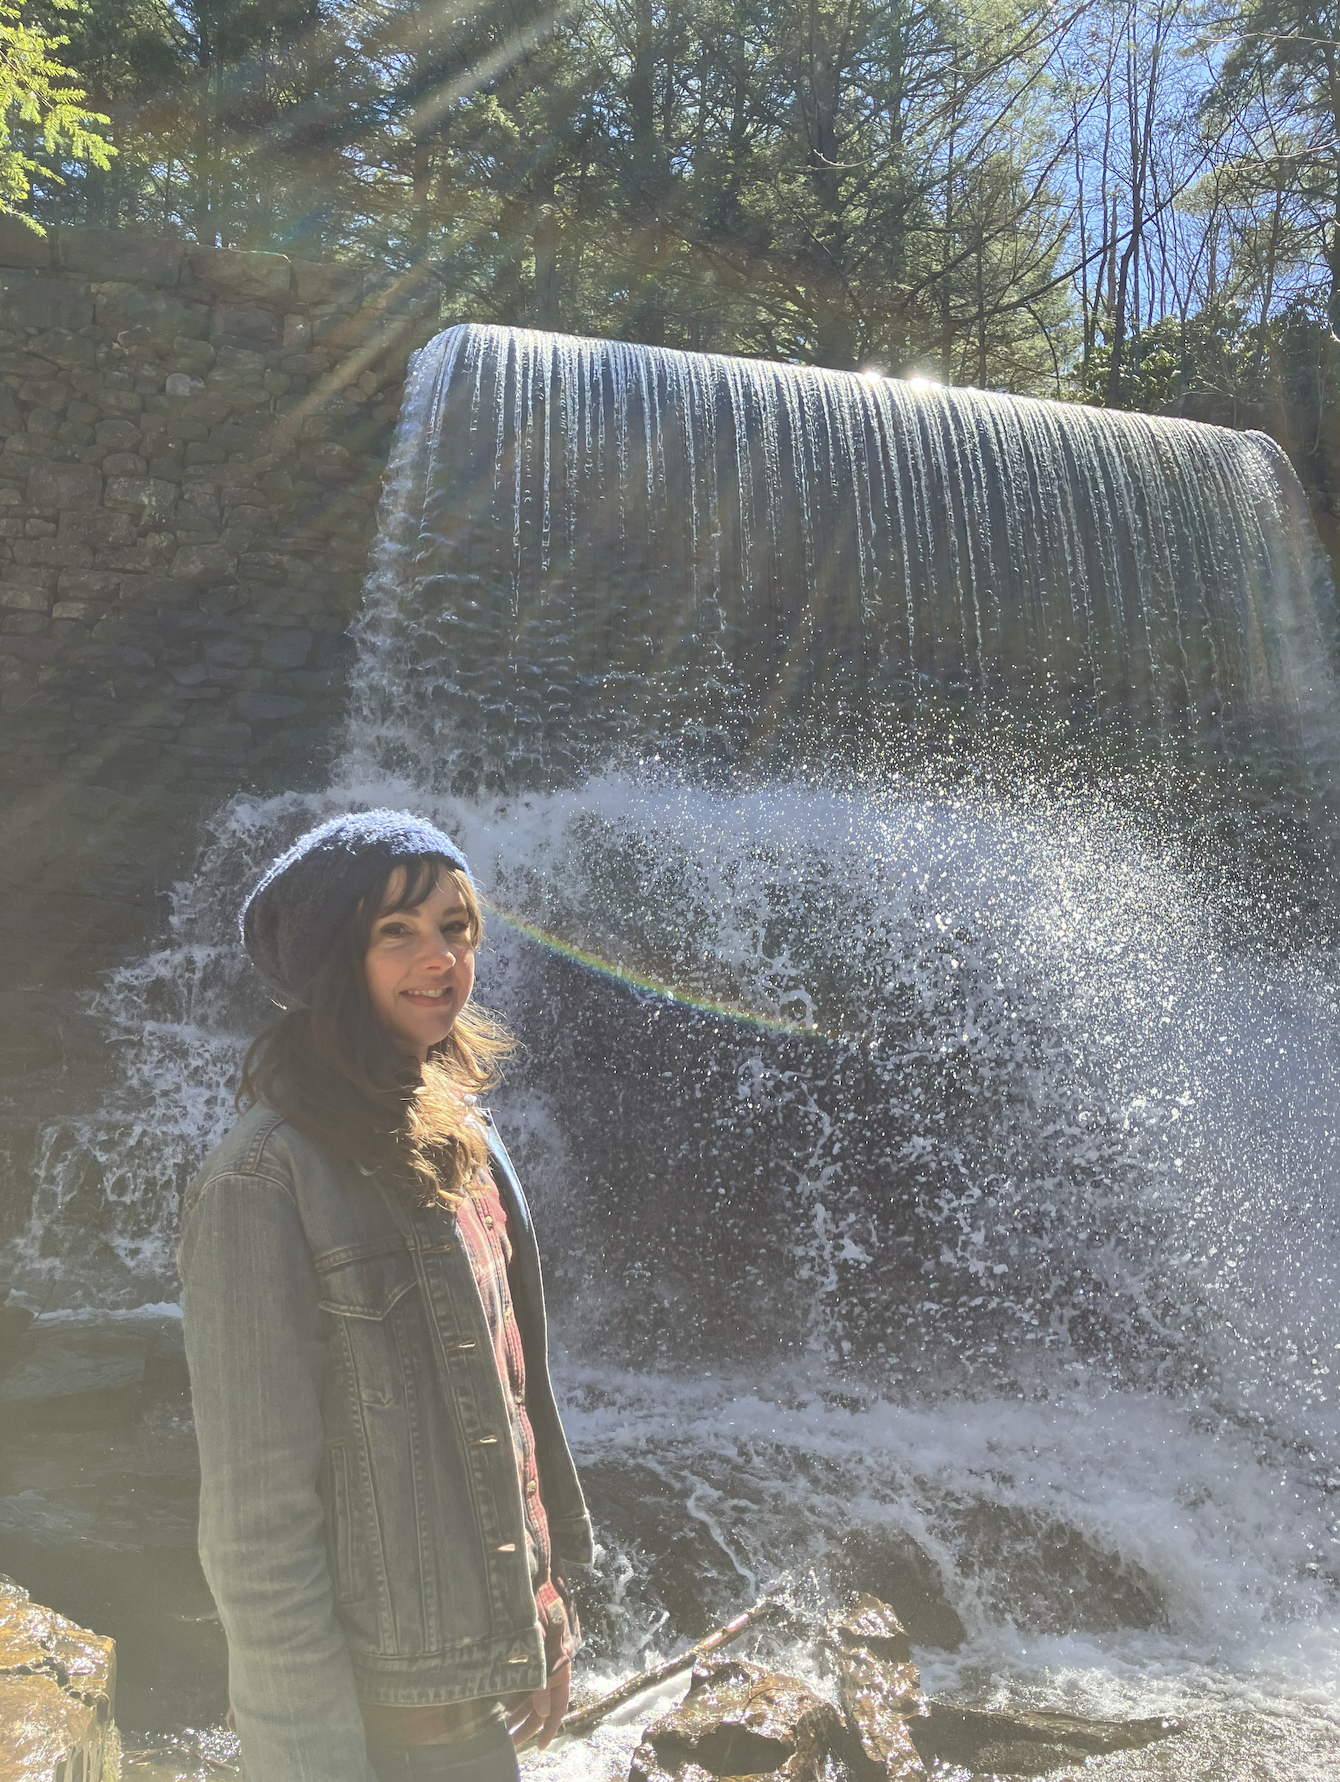
Image: Amanda Smith, courtesy of Smith.
According to a copy of the prosecuting attorney’s affidavit form, police responded to an Arkansas address on February 4 after a report of fraud. The victim said they recently found some items for sale on Facebook Marketplace. When the victim messaged about buying the items, the seller told him to send money to his wife’s CashApp account, which he did. That account was in the name Amanda Smith and had the username $Smithy5687.
It turned out, the seller’s Facebook account was hacked. The seller wasn’t really selling the items at all, and the person had been scammed. The CashApp account was created just shortly before the scam, at the end of January.
Investigators then took the CashApp account’s username and served Block Inc., which owns CashApp, with a search warrant seeking information connected to the account. The data CashApp returned included Smith’s SSN and date of birth (CashApp requires users to provide their SSN to, ironically, protect against fraud). That led investigators to the Amanda Smith, 47, who they later arrested.
Detective Poole said he then further confirmed the information on the account by obtaining a copy of Smith’s drivers’ license and “by also running her information through Accurint.” Accurint is a tool made by LexisNexis that cops use to query public and proprietary records.
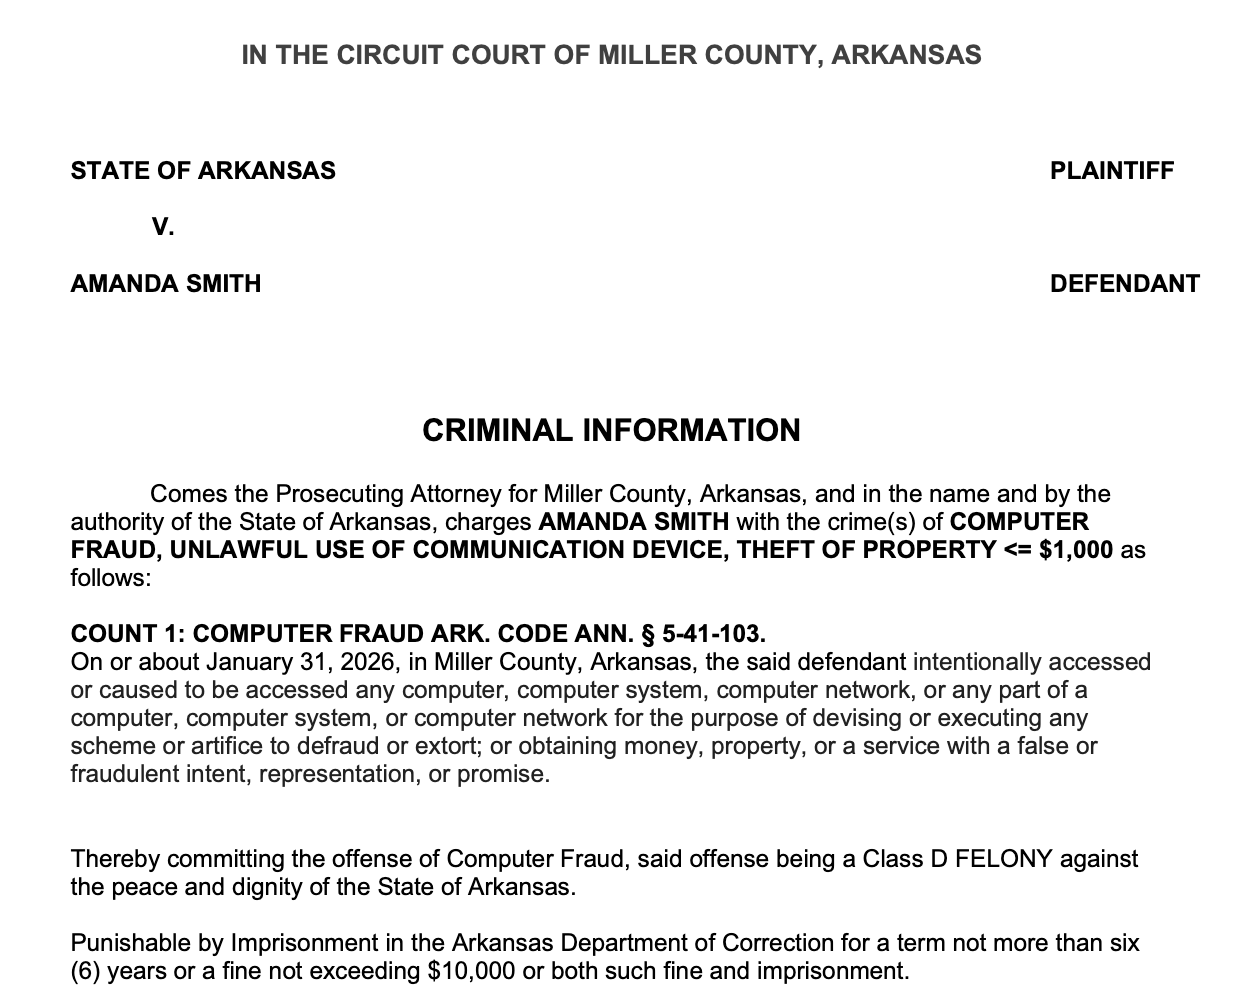
“Det [Detective] Poole sent a search warrant to Cash App. The information received from Cash App showed the account receiving the $1000 belonged to D [defendant, Amanda Smith],” the case record reads. Smith is charged with computer fraud, unlawful use of a communication device, and theft of property, according to a court filing.
“I was basically in shock,” Smith said of her three nights in the local jail. She was sleep deprived, with the lights constantly on and a guard flashing a light in her cell every hour. During that time, Smith did not actually know why she was arrested, she said. Days later she was chained and shackled and taken into court for her extradition hearing.
Her bail was set at $50,000, but Smith recalled authorities told her not to bother paying it because they intended to keep her detained to extradite to Arkansas anyway. She was released and had to make her own way to Arkansas the following week for a court appearance. Smith and her husband Josh drove, not wanting to rely on a flight’s schedule to get there, Smith said. She was nervous authorities might arrest her once again. After the hearing, authorities took Smith’s fingerprints and mugshot. After another $20,000 bail, she was free to return to Pennsylvania, but now awaits the outcome of the case. If found guilty, she could spend years in prison.
💡
Do you know anything else about CashApp fraud or similar cases to this one? I would love to hear from you. Using a non-work device, you can message me securely on Signal at joseph.404 or send me an email at joseph@404media.co.
The CashApp account was made with Smith’s SSN and date of birth, but a lot of other information from the account does not line up with Smith, according to 404 Media’s review of the data produced during discovery. The Philadelphia address on it is not Smith’s or Josh’s, nor one either of them have ever lived in. They said they lived together in Philadelphia in the same ZIP code as the address on the CashApp account, but not that address, and they don’t live in Philadelphia anymore.
Smith said the phone number used to create the CashApp account is not her current number. Her husband did not remember Smith using that phone number at all, although Smith said she may have done so in the early 2000s before she switched from T-Mobile to AT&T. 404 Media did find this phone number linked to an Amanda Smith in various data breaches from years ago using data from cybersecurity company District 4 Labs.
Using data from open source intelligence company OSINT Industries, 404 Media found someone made a Venmo account using the same phone number but under another name entirely. Whoever made that account did so around a week before the scam CashApp account.
The CashApp data also shows whoever made the account used an iPhone running 16.1.1, a very out of date operating system from 2022. Smith, however, has an iPhone 13 mini with iOS 26.5.2, according to a screenshot of her device’s settings she shared with 404 Media.
The IP addresses used during the creation of the CashApp account, and during the scam itself, relate to connections from Verizon’s wireless network, 404 Media found by querying IP geolocation tools. Again, Smith is on an AT&T plan, and says she has never had a Verizon plan.
Smith said she has never used the username “smithy5687.” 404 Media found other people online using this moniker, but none appeared to be Smith.
A screenshot of a court record in Smith's case.
Smith’s leading theory is that someone stole her identity, perhaps through a data breach like the National Public Data breach in December 2024, and used that information to open the CashApp account.
Smith only received this CashApp data through discovery in her case. When she contacted CashApp herself initially, “CashApp refused to provide me with any information about the account, because I couldn't prove that I was the owner,” she told 404 Media.
Smith hired a private investigator to review the case and data provided by CashApp. “I have been investigating the circumstances surrounding Amanda Smith’s case, and I believe there are legitimate questions about the evidence used to identify her as the person responsible for the alleged activity,” Max Ponte, the investigator, told 404 Media in an email. “The central issue is the distinction between identifying a person by name and establishing that the person actually operated or controlled an account. Based on my review of the available case materials, I have concerns about whether investigators sufficiently established that connection before pursuing criminal charges against Amanda.”
“I am actively trying to get Amanda's case dismissed short of a jury trial,” Jason Horton, Smith’s lawyer, told 404 Media in an email. “Amanda, Josh, and Mr. Ponte have provided significant information that supports Amanda's position that her charges should [be] dismissed, or, at the very least, should have been further investigated prior to Amanda's arrest. Although I do not comment on the specifics of pending cases, I will say I will do all I can to make sure justice is served in this case.”
CashApp did not respond to multiple requests for comment about the case and its verification procedures. Jeffrey Sams, the prosecutor in the case, did not respond to a request for comment asking if investigators took any additional steps to verify the CashApp data specifically beyond what was mentioned in the detective’s telling in court records.
CashApp is a common vehicle for scammers, fraudsters, and hackers. I’ve previously reported how hackers were breaking into and emptying CashApp accounts, with CashApp sometimes refusing to reimburse the stolen funds. On Telegram, many criminals offer CashApp related services, such as cashing out accounts.
In Smith’s case, it appears CashApp was the method not just to get $1,000 from a target, but also then to distribute the funds. Once the scam account received the $1,000, it sent small chunks of the money to a web of other accounts just hours later, according to the CashApp data. Some of those also appear to be scammer controlled; some of their usernames have changed from one name to a different one entirely.
Authorities have offered Smith a plea deal of a $1,000 fine, $1,000 restitution, various other costs like a bailiff and DNA sample fee, and three years probation. Smith said she refuses to accept it because she is innocent, and doing so would have long term negative consequences on her life.
“I was basically thinking, oh well, it’ll get dismissed,” Smith told 404 Media. That didn’t happen, and the case is progressing, with Smith feeling constantly anxious. A hearing is now scheduled for November.
Cisco Talos has warned that attackers abused more than 25 legitimate online platforms over the past year to deliver phishing scams through trusted email infrastructure.
The activity affected collaboration, productivity, file sharing, survey, payment, and AI services. Instead of relying only on fake domains or forged senders, criminals inserted malicious content into messages generated by legitimate systems.
These emails could pass authentication checks while carrying fraudulent phone numbers, deceptive instructions, or phishing lures.
The findings expand on earlier Talos research into platform-as-a-proxy abuse, where attackers use trusted services to deliver content they control.
That research documented phishing messages distributed through GitHub notifications and Jira invitation workflows.
Hackers Exploit Trusted Platforms
Talos examined two campaigns abusing Staples and Dell order notification systems. Together, they accounted for roughly 1,400 observed messages.
The Staples example appeared to confirm an Apple iPad purchase. It included realistic order details, pricing, delivery information, and standard branding. However, fields normally used for shipping or billing information contained a fraudulent helpline.
The Dell message followed the same pattern, presenting an unexpected Microsoft Project Standard 2024 purchase totaling $736.09. Its shipping and billing sections contained another helpline and instructions to contact a sales team.
Dell order notification (Source: talosintelligence)
Both campaigns aimed to make recipients believe an expensive purchase had already occurred. Rather than directing victims straight to a phishing website, the messages encouraged them to call attacker controlled numbers.
That shift from email to voice could enable further social engineering, payment fraud, credential theft, or remote assistance scams.
Authentication results strengthened the appearance of legitimacy. The Staples sample showed aligned DKIM and a DMARC pass, while the Dell sample also passed authentication checks.
These results verified aspects of the sending infrastructure, not the safety of the transaction details. The malicious instructions sat inside legitimate notification templates.
Talos also observed attackers repurposing list bombing, a technique that floods victims with registration or subscription emails.
In these cases, criminals entered malicious text into public forms intended for names, companies, or project titles. Automated welcome messages then repeated that input, delivering scam content through reputable services.
A third method abused delivery failure reports. One observed notification contained a WeTransfer themed lure inside returned message content.
Such messages can arise when attackers forge a victim’s envelope sender address or manipulate another sending workflow to trigger a bounce. A genuine delivery report can therefore contain an untrusted message, talosintelligence said.
Talos urged platform owners to validate user supplied values before storing them and before inserting them into emails.
Unexpected phone numbers, links, urgent language, and support instructions should be flagged when they appear in unrelated fields.
Security gateways should inspect complete messages, including nested content inside delivery reports, rather than trusting the sender alone.
Join 16,000+ SOC teams using ANY.RUN to streamline threat investigations and reduce manual effort. Explore for your team
 Log in